

Editor’s Note: The article discusses cyber resilience—an organization’s ability to anticipate, withstand, and recover from security incidents. It advocates layered security strategies, proactive planning, and monito... Read More
Missed alerts turn into outages, outages turn into lost revenue. ExterNetworks Inc. delivers 24/7 NOC & Help Desk support to keep everything running smoothly.
Get 24/7 IT Support NowCyber resilience measures how well an organization protects itself from cyberattacks. It includes physical and digital security measures, information governance policies, incident response plans, employee training, awareness programs, and processes and procedures designed to protect systems and data from unauthorized access, damage, theft, or loss.
Without a strong cybersecurity framework, organizations are open to attack, where a bad actor might gain access to networks, infrastructures, or personal computer devices, steal sensitive data, and cause significant disruption. This can majorly impact operations, resulting in lost revenue, legal issues, public relations problems, and potential lawsuits.
The goal of any cybersecurity program should be to reduce risk by protecting against threats before they occur. The best way to do this is through prevention, detection, and rapid response. Prevention means preventing attacks from happening in the first place; detection means detecting attacks as soon as possible after they happen, and rapid response means responding quickly to mitigate the effects of an attack once it has been detected.
Modern businesses depend on applications, cloud platforms, corporate networks, endpoints, and data centers to deliver products and services. A ransomware incident, compromised account, network outage, or infrastructure failure can interrupt these operations and affect customers, employees, and business partners.
Cyber resilience helps organizations prepare for these situations instead of relying exclusively on prevention.
Key business benefits include:
Cyber resilience is particularly important for organizations operating multiple locations, supporting remote employees, managing sensitive business information, or depending on continuous access to business-critical applications.
An effective cyber resilience strategy combines preventive controls with detection, response, recovery, and ongoing improvement. Each component addresses a different stage of a potential disruption.
1. Risk Assessment and Business Impact Analysis
Organizations should identify critical systems, business applications, sensitive data, network dependencies, and potential failure points.
A business impact analysis helps determine which services to restore first and how long the organization can tolerate their unavailability. This information guides recovery priorities and resource allocation.
For example, an organization may prioritize identity services, customer-facing applications, and core business databases over systems that can temporarily operate with reduced functionality.
2. Cybersecurity and Threat Prevention
Preventive security controls reduce the likelihood and impact of cyber incidents. Common measures include multifactor authentication, endpoint protection, network segmentation, vulnerability management, secure configuration, and timely patching.
Organizations should also maintain appropriate access controls and regularly review privileged accounts. These practices reduce opportunities for attackers to compromise systems or move across the network.
Prevention remains essential, but it cannot eliminate every threat. Cyber resilience ensures the organization is prepared to respond when preventive controls are bypassed.
3. Continuous IT Monitoring and Threat Detection
Continuous monitoring helps IT teams identify unusual activity, infrastructure failures, performance degradation, and other warning signs that may require investigation.
Depending on the organization’s environment, monitoring can cover network devices, servers, endpoints, applications, cloud resources, and security events.
Effective monitoring processes should include:
Monitoring does not replace dedicated security controls or incident response. Instead, it provides operational visibility that helps teams recognize problems and coordinate an appropriate response.
4. Incident Response and Escalation
An incident response plan defines how an organization identifies, investigates, contains, and manages security incidents.
The plan should specify incident severity levels, response responsibilities, communication procedures, escalation contacts, and decision-making authority.
For example, if suspicious activity affects a critical business server, the monitoring team may identify and escalate the event. At the same time, authorized security responders investigate the threat, determine containment measures, and coordinate recovery.
Clear responsibilities reduce confusion during high-pressure situations. Organizations should also establish procedures for communicating with management, affected business units, service providers, and other relevant stakeholders.
5. Backup, Disaster Recovery, and Data Restoration
Backups and disaster recovery procedures are fundamental to cyber resilience because some incidents can damage, encrypt, or make production data unavailable.
Organizations should maintain protected backups, restrict unauthorized access to backup infrastructure, and regularly test restoration procedures. Recovery plans should account for the possibility that production systems or backup credentials have been compromised.
Two important recovery objectives are:
These objectives should reflect actual business requirements and be validated through recovery testing.
6. Business Continuity Planning
Business continuity planning helps organizations maintain essential functions while systems are unavailable or being restored.
Continuity measures may include alternative communication channels, documented manual procedures, redundant infrastructure, backup connectivity, and arrangements for accessing critical applications during an outage.
The plan should identify dependencies between business processes and technology services. Restoring a database, for example, may not be sufficient if the identity platform, network connectivity, or application dependencies required to use it remain unavailable.
7. Testing, Training, and Continuous Improvement
Cyber resilience requires regular validation, not a one-time implementation.
Organizations should conduct tabletop exercises, incident response simulations, backup restoration tests, and disaster recovery exercises. These activities help identify gaps in procedures, technical controls, staffing, and communication.
After an exercise or actual incident, teams should document lessons learned, assign corrective actions, and update the relevant plans.
Enterprises can have multiple security and IT operations controls in place while still having gaps in their ability to recover from disruptions. Common weaknesses include incomplete asset inventories, unmonitored infrastructure, untested backups, excessive access privileges, unclear incident escalation responsibilities, and recovery plans that do not account for system dependencies.
Businesses should regularly review these gaps across networks, endpoints, applications, cloud environments, and third-party services. Prioritizing weaknesses according to business impact helps IT and security teams focus resources on the systems and processes most critical to continuity.
Continuous IT monitoring supports cyber resilience by improving visibility into the health and availability of business-critical infrastructure. It helps organizations identify technical problems, recognize unusual events, and route incidents to the teams responsible for investigation and resolution.
For businesses operating complex networks or multiple locations, monitoring can help identify issues such as:
A Network Operations Center (NOC) can support these operational requirements through infrastructure monitoring, alert triage, incident escalation, and coordination with internal IT teams.
However, infrastructure monitoring and security operations are not interchangeable. A NOC may identify availability problems or suspicious operational patterns, while dedicated security personnel and security monitoring capabilities may investigate threats, perform threat hunting, and coordinate containment.
Organizations should define the responsibilities of their internal IT teams, security teams, and external service providers before an incident occurs.
Network resilience supports cyber resilience by helping maintain reliable connectivity between business locations, applications, users, and critical infrastructure during disruptions. Redundant connections, resilient network architectures, appropriate segmentation, configuration backups, and tested failover procedures can reduce the impact of individual network failures.
Network monitoring also helps IT teams identify connectivity problems, device failures, and unusual performance changes that require investigation. When an incident affects critical services, clear escalation procedures and coordination with security and recovery teams help organizations determine the appropriate response.
Network resilience alone does not guarantee protection against cyberattacks. It should complement access controls, security monitoring, incident response, and recovery planning.
Businesses can strengthen cyber resilience through a structured process that connects risk management, operational monitoring, incident response, and recovery.
Step 1: Identify Critical Business Services
Inventory the applications, infrastructure, data, and third-party services required to support essential business processes.
Classify these resources according to business impact, recovery requirements, and dependencies.
Step 2: Assess Existing Risks and Gaps
Review current security controls, access management, network architecture, backup arrangements, monitoring coverage, and incident response procedures.
Identify single points of failure and determine whether existing controls support the organization’s recovery objectives.
Step 3: Establish Recovery and Escalation Priorities
Define RTOs, RPOs, incident severity levels, escalation paths, and ownership for critical services.
Make sure technical recovery targets align with business requirements and that decision-makers understand their responsibilities.
Step 4: Improve Monitoring and Incident Coordination
Ensure critical systems are monitored and that alerts reach the appropriate teams.
Establish clear handoffs between infrastructure operations, security responders, application owners, and business stakeholders. Document when to escalate incidents and who can authorize containment or recovery actions.
Step 5: Protect and Test Recovery Capabilities
Maintain appropriately protected backups and test whether you can restore critical applications, data, and supporting infrastructure.
A backup should not be considered reliable solely because a scheduled backup job completed successfully.
Recovery tests should confirm that the team can use the data and bring the required systems back into operation.
Step 6: Conduct Exercises and Improve the Plan
Run realistic incident scenarios, document the results, and correct identified weaknesses.
Review the plan whenever significant changes occur in the organization’s infrastructure, applications, suppliers, or business requirements.
Measure cyber resilience using a combination of security, operational, and recovery metrics. No single metric can demonstrate that an organization is fully resilient.
Useful measures include:
| Metric | What it measures | Why it matters |
|---|---|---|
| Mean Time to Detect (MTTD) | Average time taken to identify an incident | Indicates how quickly issues become visible |
| Mean Time to Respond (MTTR) | Time taken to respond to an incident, using a consistently defined start and end point | Helps evaluate response efficiency |
| Mean Time to Recover | Time required to restore affected services | Shows how quickly operations return |
| RTO achievement | Whether recovery meets the established time objective | Evaluates recovery performance against business needs |
| RPO achievement | Whether recovery meets the established data-loss objective | Evaluates data recovery against business needs |
| Backup restoration success rate | Percentage of tested restorations completed successfully | Helps validate recovery readiness |
| Critical service availability | Availability of business-critical systems | Measures continuity of essential services |
| Incident recurrence rate | Frequency of repeated incidents caused by unresolved issues | Helps identify weaknesses in corrective actions |
Organizations should define each metric consistently, establish a baseline, and track trends over time. Faster recovery is not the only objective: a successful resilience program must also preserve data integrity, maintain appropriate security, and restore services in a controlled manner.
Businesses can test cyber resilience through structured exercises that evaluate whether their teams, technology, and recovery procedures work as expected during a disruption.
Common testing methods include:
After each exercise, document gaps, assign corrective actions, and retest important weaknesses. Authorize and plan testing to avoid unnecessary disruption to production services.
Cyber resilience services help organizations strengthen their ability to prepare for, manage, and recover from cyber-related disruptions. Depending on the provider and engagement scope, these services may include resilience assessments, security monitoring, incident response support, backup and recovery planning, disaster recovery testing, and business continuity preparation.
When evaluating a provider, businesses should clarify which capabilities are included and which remain the responsibility of internal teams or other vendors.
For infrastructure-focused support, relevant capabilities may include:
These capabilities can contribute to a broader cyber resilience strategy, but they should not be confused with a complete cybersecurity or incident response program.
Before selecting a provider, organizations should assess the provider’s capabilities against their operational requirements.
Consider the following questions:
Businesses should request clear documentation of service scope, exclusions, response commitments, reporting requirements, and incident ownership before signing an agreement.
Cybersecurity and cyber resilience are often used interchangeably, but they serve different purposes within an organization’s overall security strategy. While cybersecurity focuses on preventing and defending against threats, cyber resilience emphasizes maintaining operations and recovering quickly in the event of incidents. The table below highlights the key differences between the two.
| Aspect | Cybersecurity | Cyber Resilience |
|---|---|---|
| Primary Goal | Prevent cyber attacks and breaches | Ensure business continuity despite attacks |
| Approach | Proactive Defense | Proactive + Reactive (Prepare, Respond, Recover) |
| Mindset | “Stop the Attack” | “Assume breach and minimize impact” |
| Focus Area | Systems, Networks, Data Protection | Entire business operations and continuity |
| Scope | Mostly technical controls | Technical + Operational + Business Processes |
| Key Activities | Firewalls, Encryption, Access Control, Patching | Backup, Disaster Recovery, Incident Response, Business Continuity |
| When It Acts | Before an attack | Before, during, and after an attack |
| Outcome | Reduced risk of incidents | Faster recovery and minimal disruption |
| Measurement | Number of prevented/detected threats | Recovery Time, Downtime, Business Impact |
| Example | Blocking malware or unauthorized access | Restoring systems quickly after a ransomware attack |
The NCSC published a report earlier this week outlining how businesses can improve cyber resilience. The report focuses on four key areas: preparing for attacks, absorbing damage during attacks, recovering quickly and efficiently, and adapting to changes over time.
For example, many cloud providers offer customers access to their infrastructure without requiring them to provide credentials. This makes it easier for hackers to gain access to sensitive information.
In conclusion, cyber resilience is critically important in any organization’s overall cybersecurity strategy. By taking the time to understand and implement these principles, organizations can create a foundation for enduring success in the digital age.
Cyber resilience is the ability of an organization to continue functioning in a digital world. It’s about adapting and responding quickly when things go wrong, or even better, anticipating problems before they happen. In other words, it’s about having the right people, processes, technology, policies, and culture to ensure that your business can withstand cyber threats and remain operational.
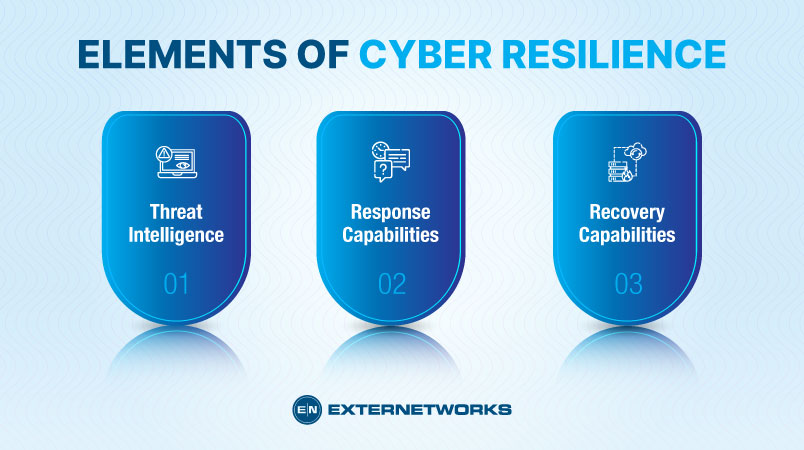
There are three key elements to achieving cyber resilience:
Threat intelligence is collecting, analyzing, and disseminating information on potential threats. The goal is to identify what attackers are doing, where they are coming from, and what vulnerabilities they might exploit.
Response capabilities are the methods an organization uses to detect, prevent, and mitigate threats. This includes everything from firewalls and IDPs to DLP software and antivirus solutions.
Recovery capabilities refer to the procedures an organization uses to restore normal operations after a threat has occurred. This includes everything from disaster recovery plans to backup data and protection against outages.
Cyber resiliency has many benefits, including:
You can reduce the cost of cyber attacks by implementing proper controls at every process stage. You can deploy anti-malware software to scan incoming files before reaching your mainframe. You can also set up an alert system to notify administrators of unauthorized activity. This will help you identify potential threats early and take action before a breach becomes serious.
You can improve productivity by reducing downtime caused by failed hardware or network connections. When employees have access to secure resources, they can focus on their jobs instead of worrying about whether their computer is working properly.
Increased customer satisfaction comes from providing better service and faster response times. Customers appreciate being informed about any changes to your company’s security posture, and they also like knowing that their personal information is safe.
Finally, improving employee morale helps everyone operate more efficiently. Motivating people is easier when they know their efforts are making a difference.
At ExterNetworks, we understand the importance of staying one step ahead in the ever-evolving landscape of cyber threats. With our proactive monitoring services, you can rest easy knowing that potential threats are being identified and addressed before they can impact your organization. Our team of cybersecurity experts brings years of experience to the table, ensuring that your systems are always protected against the latest threats.
We offer customized solutions to fit your unique cybersecurity needs, ensuring you receive the level of protection your organization requires. Additionally, we help keep your organization compliant with industry regulations and standards, giving you peace of mind knowing that your data is secure.
By choosing ExterNetworks for cyber threat monitoring services, you can save on the costs of hiring an in-house security team while benefiting from top-notch protection. Don’t wait until it’s too late—contact ExterNetworks today to learn more about how our services can benefit your organization.
See how ExterNetworks can help you with Managed NOC Services
Contact Us







