 NOC Services
Inside a US NOC: How Cybersecurity Threats Are Detected and Mitigated in Real-Time


Editor’s Note: This article takes readers inside a US-based Network Operations Center (NOC), highlighting how real-time monitoring, advanced technology, and skilled professionals work together to defend businesses f... Read More
Downtime Draining Your Business? Fix It Before It Costs More
Missed alerts turn into outages, outages turn into lost revenue. ExterNetworks Inc. delivers 24/7 NOC & Help Desk support to keep everything running smoothly.
Get 24/7 IT Support NowIntroduction
Understanding the Role of a Network Operations Center (NOC)
A Network Operations Center (NOC) is the pulsating heart of an organization’s IT infrastructure. Acting as a centralized hub, it is responsible for monitoring, managing, and maintaining a network’s performance and ensuring optimal functionality.
In the context of cybersecurity, a NOC deploys advanced technologies and a skilled workforce to detect cybersecurity threats, enabling organizations to preemptively respond to potential breaches.
NOCs are crucial for maintaining the operational integrity of network systems, ensuring that data—widely regarded as the new oil—remains safe and secure from malignant forces.
The Escalating Need for Real-Time Cybersecurity Monitoring
As cyber threats become increasingly sophisticated and pervasive, the importance of real-time cybersecurity monitoring cannot be overstated. Attacks that once took weeks or months to manifest can now unfold in a matter of minutes, rendering traditional methods of threat detection obsolete.
Organizations must pivot to a proactive approach that prioritizes real-time monitoring, allowing them to rapidly identify and neutralize threats before they metastasize into full-blown security breaches.
This approach not only minimizes potential damage but also significantly reduces recovery costs and safeguards a company’s reputation.
Importance for IT Managers and Business Owners
The role of real-time monitoring in cybersecurity extends beyond mere technical necessity; it provides IT managers and business owners with transparency and peace of mind. For IT managers, it means having a vigilant eye on the network’s health and security, ensuring that any anomalies are immediately addressed.
Meanwhile, business owners gain a clearer understanding of their organization’s security posture, allowing for informed decision-making and strategic planning.
In an era where data breaches are headline news, being informed and prepared is vital to maintaining stakeholder confidence and market competitiveness.
Preview of the Exploration into Tools, Workflow, and Real-World Examples
This blog post will delve into the indispensable tools and streamlined workflows that underpin effective NOCs in the United States.
We will explore real-world examples that illustrate how these centers successfully detect and thwart cybersecurity threats around the clock.
By examining these elements, readers will gain insight into the complexities involved in maintaining cybersecurity vigilance and the advanced resources employed to mitigate risks.
This understanding not only enriches one’s knowledge of NOC operations but also underscores the critical importance of investing in robust cybersecurity infrastructures.
What is a NOC?
A Network Operations Center (NOC), pronounced “knock,” is a pivotal component in robust IT infrastructure management. Essentially, it serves as the strategic command hub, operating 24/7, where skilled IT professionals oversee, monitor, and manage complex technology environments.
This constant vigilance ensures that businesses experience minimal disruptions, maintain optimal performance, and effectively safeguard digital resources against potential threats. By harnessing cutting-edge technology and real-time data, the NOC acts as the central nervous system of an organization’s IT operations.
Key Responsibilities of a NOC
To better understand the intricacies of a NOC, consider its core responsibilities, which ensure the smooth functioning of an organization’s IT framework.
Monitoring Network Traffic for Anomalies
One of the primary duties of a NOC is to monitor network traffic consistently. By analyzing data flow throughout an organization’s networks, NOC technicians can identify and address anomalies swiftly.
This capability is crucial for preempting potential issues before they impact the business. By using advanced analytics tools, they detect unusual patterns that may indicate security breaches or performance degradations, thereby averting potential crises.
Detecting Downtime, Breaches, and Performance Issues
Another critical role of a NOC is the early detection of downtime, security breaches, and other performance-related issues. By employing sophisticated monitoring software, the NOC is able to pinpoint problems as soon as they arise.
This proactive approach not only helps in mitigating risks but also minimizes downtime, thereby ensuring businesses remain operational and productive. Prompt identification and resolution of these challenges is key to maintaining customer trust and organizational efficiency.
Coordinating with Security Operations Centers (SOC) When Needed
Although a NOC primarily focuses on network performance and reliability, it often collaborates with Security Operations Centers (SOC) when security threats are detected. This collaboration allows for a more comprehensive analysis and swift response to incidents.
When a NOC identifies a potential security threat, it coordinates with the SOC to ensure a specialized approach to threat neutralization. This collaboration ensures that all aspects of IT infrastructure, including security and performance, are seamlessly managed.
Brief Comparison: NOC vs. SOC
While both NOCs and SOCs are integral to a company’s IT infrastructure, they serve distinct yet complementary functions. The NOC is focused on network performance, ensuring that systems run smoothly and efficiently.
In contrast, a SOC is solely dedicated to security, monitoring for potential threats, and responding to cyber-attacks. Essentially, the NOC ensures that the infrastructure functions correctly, while the SOC ensures it is secure from malicious activities.
Both centers work in tandem to provide an integrated approach to IT management, each addressing critical aspects of technology operations and security.
How a NOC Detects Cybersecurity Threats in Real-Time
The Uninterrupted Data Stream: Insights from NOC Engineer Dashboards
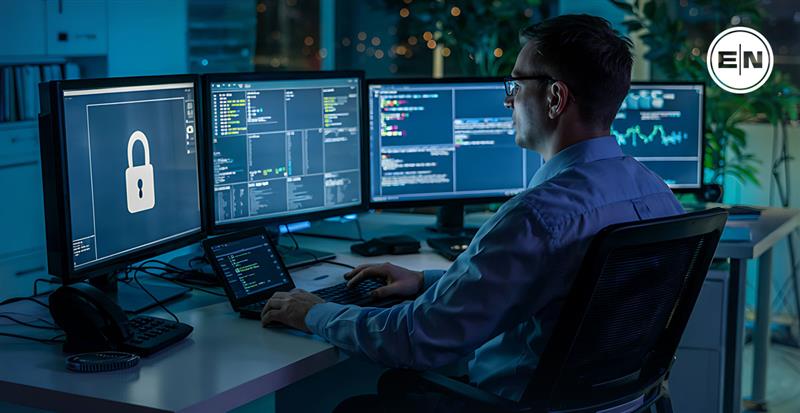
To successfully detect cybersecurity threats in real time, Network Operations Center (NOC) engineers rely heavily on a continuous flow of data streaming across their dashboards.
These dashboards serve as the nerve center for monitoring network activities and are equipped with advanced visualization tools that display core metrics such as data flow patterns, server statuses, and user activities.
Engineers are trained to interpret these complex data streams swiftly, identifying anomalies that could indicate potential threats. Given the sheer volume and velocity of data, the ability to distinguish meaningful patterns is both an art and a science, requiring deep technical knowledge and keen analytical skills.
Differentiating “Threats” from “Noise” in Network Traffic
Amidst the continuous data flow, differentiating legitimate threats from benign network noise is crucial. Network behavior is inherently noisy, with numerous fluctuations and irregularities that often occur under normal operational circumstances.
However, threats are characterized by specific patterns that deviate significantly from this typical noise.
For instance, an unusual access request from a geographic location that historically has been non-communicative with the network might raise a red flag.
Skillful NOC engineers are adept at defining and refining these parameters, allowing for the seamless differentiation between what constitutes a real threat and what is mere background noise.
Identifying Anomalies: Patterns That Trigger Alerts
Anomalies in network behavior can take numerous forms, each potentially signaling a distinct type of cybersecurity threat. Firstly, sudden traffic spikes can indicate a Distributed Denial of Service (DDoS) attack, where the network is flooded with an overwhelming amount of requests.
Secondly, interactions with suspicious IP addresses can suggest attempts at data breaches from known threat actors. Thirdly, port scanning activities—where multiple ports are rapidly checked for vulnerabilities—often precede more sophisticated attacks.
Lastly, unauthorized login attempts may highlight ongoing efforts to compromise user accounts. Each of these anomalies necessitates swift identification and further analysis to preempt any detrimental impact on network security.
Proactive Measures: Alert Systems and Escalation Protocols
To manage these threats effectively, alert systems and escalation protocols are integral components of a NOC’s cybersecurity framework. Alerts are triggered automatically when specific thresholds are crossed or when suspicious activities are detected.
These alerts are categorized based on severity, ensuring that potentially catastrophic threats are prioritized. Once an alert is triggered, predefined escalation protocols come into play. These protocols outline the series of steps that need to be taken to address the threat, involving various stakeholders and decision-makers.
Furthermore, constant refinement of alert thresholds and escalation processes ensures that the NOC remains resilient and responsive in the ever-evolving landscape of cyber threats.
What tools are commonly used inside a NOC?
A NOC typically uses a combination of network monitoring platforms, SIEM systems, IDS/IPS tools, AI-driven analytics, behavioral monitoring, dashboards, and ITSM platforms to maintain visibility across the IT environment. These tools help NOC teams monitor infrastructure, identify anomalies, correlate events, prioritize alerts, and coordinate incident response.
Common tool categories include SIEM platforms such as Splunk, IBM QRadar, and ArcSight for centralized log collection and event correlation. IDS/IPS solutions such as Snort and Suricata can help identify and prevent suspicious network activity. At the same time, AI-driven analytics and behavioral monitoring establish normal activity patterns and flag deviations for investigation.
NOC teams also rely on real-time monitoring dashboards to visualize network traffic, server status, user activity, alerts, and infrastructure health. These dashboards give engineers a centralized operational view and help them quickly distinguish meaningful events from normal network activity.
For enterprise operations, these monitoring tools are typically combined with ITSM and escalation workflows so that validated incidents can be logged, prioritized, escalated, resolved, and documented consistently.
Tools Used for Real-Time Threat Detection
In today’s rapidly evolving digital landscape, robust real-time threat detection tools are more critical than ever. Cyber threats are becoming increasingly sophisticated, and organizations must leverage advanced mechanisms to protect their data and systems. Here, we explore some of the most effective tools for real-time threat detection.
Security Information and Event Management (SIEM) Systems
SIEM systems are pivotal in cybersecurity because they provide a comprehensive approach to real-time threat detection. One of SIEM’s primary functions is to aggregate logs from diverse systems in real time. This aggregation gives security teams a centralized view of all security events across the network, simplifying monitoring.
Moreover, SIEM systems excel in correlating events to spot suspicious patterns. By analyzing various logs and security events, SIEM can identify anomalies that might signify security threats, enabling proactive responses.
Popular platforms such as Splunk, IBM QRadar, and ArcSight have set the benchmark for SIEM technologies. These platforms offer a suite of tools designed to enhance visibility and streamline the identification of potential security breaches. Additionally, they often integrate with various security applications, enhancing their ability to provide a holistic security perspective.
Intrusion Detection and Prevention Systems (IDS/IPS)
Intrusion Detection Systems (IDS) and Intrusion Prevention Systems (IPS) are integral components of any comprehensive cybersecurity strategy. An IDS performs the crucial role of monitoring network traffic for malicious activities and logging potential threats.
Unlike IDS, an IPS goes a step further by actively blocking identified threats before they can penetrate and damage the network. This proactive defense capability is vital in mitigating immediate security risks.
Snort and Suricata are excellent examples of widely adopted IDS/IPS tools. Snort, a free and open-source network intrusion detection and prevention tool, is renowned for its versatility and strong community support. Similarly, Suricata is valued for its high-performance capabilities and ability to detect complex threats across large networks.
AI-Driven Analytics and Behavioral Monitoring
Artificial intelligence (AI) is revolutionizing threat detection through AI-driven analytics and behavioral monitoring. By using machine learning algorithms, these systems establish a baseline of “normal” user behavior within an organization.
The system continuously updates and refines this baseline as it observes routine activities.
Whenever deviations from the norm occur, the system flags these anomalies for further examination. What’s impressive is that the AI engine learns from each detection, making it increasingly adept at identifying new threats over time.
This autonomous adaptability means that such systems are not only faster but also far more scalable than traditional human-only security teams. This makes AI-driven analytics and behavioral monitoring indispensable in handling the complexities of modern cybersecurity threats.
As cyber threats continue to evolve, so must the tools used to combat them. By using SIEM systems, IDS/IPS solutions, and AI-driven analytics, organizations can better safeguard their digital assets and maintain network integrity.
How NOC Analysts Separate False Alarms from Real Threats
Effectively distinguishing between false alarms and genuine threats is one of the critical tasks for Network Operations Center (NOC) analysts. These skilled professionals use a structured triage process to ensure resources focus only on issues that truly matter. Understanding the nuanced stages of this process can highlight the importance of prompt, accurate threat differentiation.
A Deep Dive into the Triage Process
The triage process is segmented into three distinct levels, each playing a vital role in handling potential threats:
Level 1: Alert Identification and Logging
The first level involves the Level 1 analyst, the initial point of contact. This individual identifies and meticulously logs every alert that surfaces. By maintaining a detailed record, the Level 1 analyst lays the groundwork for further investigation.
This logging process is essential for maintaining historical data, which can be invaluable for recognizing recurrent patterns or anomalies over time.
Level 2: Contextual Investigation and Risk Validation
Once an alert is logged, it moves to a Level 2 analyst, whose job is to dig deeper into the alert’s context. This analytical step involves validating whether the alert indicates a real risk.
Level 2 analysts have the skills to interpret more complex data and evaluate the threat’s significance based on context. Using advanced tools and techniques, they scrutinize the data to distinguish malicious activity from benign activity, minimizing unnecessary escalations.
Level 3: Issue Mitigation and Documentation of Resolution
Level 3 analysts handle the final stage of the triage process, focusing on mitigating confirmed threats. Once a risk is validated as genuine, analysts take swift action to neutralize the issue and prevent potential damage.
After mitigation, these analysts must comprehensively document the resolution process. Detailed documentation not only ensures compliance with security protocols but also builds the team’s collective knowledge, forming a foundation for stronger future response strategies.
Unveiling Common Sources of False Positives
Certain conditions are notorious for generating false positives, frequently diverting attention needlessly:
Legitimate Software Updates
One common cause of false alarms is legitimate software updates. These updates can sometimes resemble suspicious activity because of the volume and nature of the data they generate. NOC analysts must be adept at quickly identifying these updates to avoid unnecessary alarms.
Internal Testing or Misconfigured Rules
Similarly, internal testing activities or misconfigured security rules can trigger false positives. Such instances require a keen eye and a deep understanding of the network environment. Analysts must adjust or calibrate system settings to better distinguish between testing scenarios and potential threats.
Why would an enterprise use a US-based NOC?
Enterprises may choose a US-based NOC when they need continuous network monitoring, faster incident coordination, and operational support for critical IT infrastructure. A dedicated NOC provides around-the-clock visibility into network performance, helping organizations identify anomalies, downtime, and performance issues before they significantly affect business operations.
For enterprises operating across multiple locations, a US-based NOC can also provide centralized monitoring and escalation for distributed infrastructure. NOC teams can coordinate incident response, work with internal IT teams and other service providers, and escalate security-related events to a SOC when specialized investigation is required.
The business value extends beyond monitoring. Continuous NOC operations can reduce operational disruption, support business continuity, and let internal IT teams focus on strategic initiatives rather than constantly monitoring network events. The source specifically emphasizes the role of a dedicated NOC in proactive risk management, continuous monitoring, and maintaining business operations.
For an enterprise considering a US-based NOC, the decision should ultimately be based on its network complexity, uptime requirements, geographic footprint, incident-response needs, and requirement for continuous operational coverage.
How does a US NOC operate?
A US NOC operates as a centralized, continuously monitored environment where NOC engineers oversee network activity, infrastructure performance, and operational alerts. Monitoring systems collect real-time data and display network traffic, server status, and other operational indicators through centralized dashboards.
When an anomaly or alert is detected, NOC analysts investigate the event and determine whether it represents a genuine operational or security issue. Alerts are prioritized by severity, and predefined escalation procedures determine which teams or decision-makers to involve.
The process generally follows a structured workflow of detection, investigation, validation, escalation, mitigation, and documentation. Level 1 analysts identify and record alerts, while Level 2 analysts investigate the context to assess and confirm risks. Level 3 analysts focus on addressing validated issues and ensuring that the resolutions are thoroughly documented.
When an event involves a potential cybersecurity threat, the NOC can coordinate with the SOC for specialized investigation and response. This lets the NOC stay focused on network performance and operational reliability while the SOC handles deeper security analysis.
The result is a proactive operating model in which continuous monitoring, automated alerts, analyst expertise, escalation procedures, and documented response processes work together to maintain network availability and reduce operational disruption.
The Role of Human Expertise and Correlation
While automated systems are invaluable in processing vast amounts of data, human expertise is irreplaceable for precise threat detection. Experienced NOC analysts bring a critical layer of intelligence that automation alone cannot provide. They use nuanced judgment and correlate various data points to distinguish harmless anomalies from genuine threats.
This expertise is indispensable in a dynamic threat landscape, ensuring networks are safeguarded against intrusions without falling prey to the inefficiencies of chasing false alarms.
Real-World Examples of Incident Response Workflows
Effectively managing cybersecurity incidents is essential for safeguarding an organization’s digital assets. To better understand the practical application of incident response, we examine several case studies that highlight successful workflows in real-world scenarios. Through these examples, one can appreciate how structured responses can mitigate and even prevent data breaches.
Example 1: Malware Detected Through SIEM Correlation
When a Security Information and Event Management (SIEM) tool flags multiple failed login attempts across several endpoints, it acts as an early warning system for potential security breaches.
In one notable case, an IT analyst leveraged the SIEM tool to trace the source of these suspicious activities back to a phishing email. Recognizing this as a critical threat vector, the response team quickly isolated the affected machines to prevent further spread.
This decisive action was coupled with a reset of compromised credentials, effectively neutralizing the threat and protecting the network from further harm.
Example 2: Defending Against a DDoS Attack
A sudden spike in network traffic can signal a Distributed Denial of Service (DDoS) attack, as shown in another case study. Upon noticing an unusual surge in network traffic on their dashboard, an analyst acted promptly to verify the source of the anomaly.
Realizing the organization was under a DDoS attack, the analyst swiftly implemented rate-limiting rules on the firewall to mitigate the impact. The analyst also contacted the Internet Service Provider (ISP) to request upstream filtering, ensuring excessive traffic was managed before it could overwhelm the organizational network.
This comprehensive response effectively minimized downtime and maintained service availability.
Example 3: Detecting Insider Threats
Organizations often face threats not just from external actors but also from within. In a compelling example of insider threat detection, an AI-based tool alerted the organization to anomalous file access patterns initiated by a remote employee.
The Network Operations Center (NOC) quickly escalated this issue to the Security Operations Center (SOC) for a deeper investigation. Forensic analysis unveiled an exfiltration attempt, confirming the employee’s malicious intent.
As a result, the organization immediately revoked the employee’s access, effectively blocking the threat and preserving sensitive data. This case underscores the importance of utilizing advanced tools to detect and prevent insider threats.
Through these diverse examples, it becomes evident that timely detection, coordinated response, and leveraging advanced tools are integral to effective incident response workflows.
These case studies not only highlight the need for a robust security posture but also demonstrate the importance of having well-defined processes in place to respond effectively to various types of cyber incidents.
Conclusion
The Value of Real-Time Threat Mitigation in a US-Based NOC
A Comprehensive Approach: Integrating Tools, Expertise, and Processes
Real-time threat mitigation within a US-based Network Operations Center (NOC) hinges on a seamless integration of advanced technology, skilled professionals, and robust procedural frameworks.
On one hand, advanced tools and technologies serve as the frontline defenses, providing indispensable features such as intrusion detection, traffic analysis, and threat intelligence.
On the other hand, skilled experts, who possess in-depth knowledge and a watchful eye, interpret complex data and make real-time decisions that technology alone cannot handle.
Moreover, structured processes standardize responses to incidents, ensuring that the NOC operates efficiently and effectively at all times. Together, these elements enable a NOC to identify and respond to potential threats with unparalleled precision.
The Significance of Proactive and Transparent Cybersecurity
The role of a NOC extends far beyond merely reacting to threats. It is about adopting a proactive cybersecurity posture that prioritizes anticipating potential risks before they manifest as actual threats.
By leveraging predictive analytics and threat forecasts, a NOC can identify vulnerabilities within systems and patch them preemptively, consequently reducing the likelihood of a successful cyber attack.
Furthermore, transparency in cybersecurity practices is crucial. Whenever stakeholders—ranging from IT managers to end users—are informed promptly and openly about the security measures being implemented, a culture of trust and awareness is cultivated.
This not only enhances the organization’s cyber resilience but also reassures all parties that their data is handled with utmost care.
Assuring IT Managers and Business Owners: Effective Risk Management is Feasible
Undoubtedly, the digital landscape presents numerous challenges, yet the right systems can manage these risks effectively. For IT managers and business owners, the presence of an adept NOC provides significant relief and assurance.
With a dedicated team monitoring networks round-the-clock, potential threats are scrutinized and neutralized before they escalate into crises.
This proactive risk management approach reinforces the confidence of stakeholders, allowing them to focus on core business functions without the looming anxiety of potential security breaches.
By investing in comprehensive NOC solutions, organizations can mitigate risks while ensuring business continuity and safeguarding their reputation. As a result, IT managers and business owners can rest assured that their cybersecurity challenges are being addressed expertly and efficiently.
Need Transparency and Protection Around The Clock?
Discover how ExterNetworks’ US-based NOC keeps your infrastructure secure 24/7. Contact Us Today for a Free Consultation or Demo.
Related on ExterNetworks Right Now!